Governance · Risk · Cybersecurity · Compliance
James O'Donnell
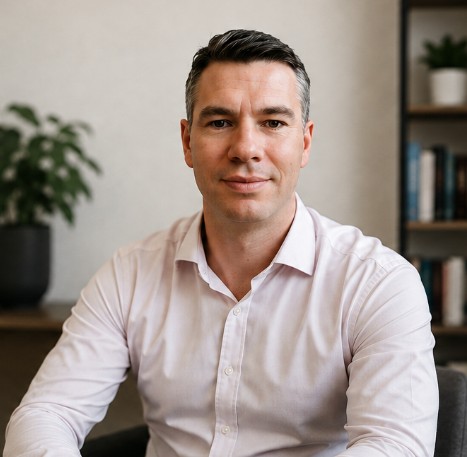
I've always worked where systems, standards and people meet.
First in quality. Then IT. Now governance, risk and cybersecurity.
Based in Wicklow, Ireland · Open to the right governance, risk, assurance and cybersecurity opportunities.
About
17 years building systems
that stand up to scrutiny
My career has moved across engineering, quality management, IT and governance. The common thread has been making complex requirements work in practice — building processes, implementing controls, assessing effectiveness and giving stakeholders confidence that things are being done properly.
I started on major international energy and infrastructure projects, moved into management systems and audit, and then spent more than eight years managing IT infrastructure and security controls across a multi-location organisation.
Today I bring those experiences together across governance, technology risk, cybersecurity, compliance and assurance.
Projects
Things I've strengthened
Identity · Security · Microsoft 365
Identity & Access Governance
Implemented organisation-wide MFA, Conditional Access and structured joiner-mover-leaver controls across Microsoft 365 and Azure AD. Monitored risky sign-ins, managed permissions and applied role-based access principles to reduce identity risk.
→ Security controls designed around real business workflows
IT Operations · RMM · Resilience
Endpoint Visibility & Control
Researched, selected and implemented Atera RMM to centralise endpoint visibility, patch status, asset information and remote support across distributed project locations.
→ Better visibility, standardisation and operational control
Governance · Audit · ISO 9001
Management Systems & Assurance
Led risk-based audit programmes, corrective action processes, risk and opportunity management, performance reporting and management-system improvement across international operations.
→ Governance translated into evidence, ownership and action
Risk · Evidence · Commercial Impact
Evidence-led Risk Resolution
Challenged a major project non-conformance with potential exposure of approximately £1.2m by coordinating independent testing and presenting evidence directly to senior client stakeholders.
→ Technical evidence used to resolve risk and avoid unnecessary rework
Experience
Where I've worked
2024 — Present
Quality & Compliance Manager
Ardale Construction · Ireland
Building structured governance, quality and compliance processes in a live residential construction environment, including management-system development, audits, document control, regulatory compliance and corrective action.
2016 — 2024
IT Manager
Randridge International · Multi-location
Managed Microsoft 365, identity and access, endpoint monitoring, backups, virtualisation, network security, security awareness, IT procedures and operational support across international project locations.
2013 — 2016
Group Quality Manager
Randridge International · International
Led management-system governance, internal audit programmes, risk and opportunity processes, corrective action, KPI reporting, certification activity and continual improvement.
2009 — 2013
Project Quality Leadership
Major energy & infrastructure projects · UK, Kazakhstan, Canada & Qatar
Quality assurance, inspection coordination, compliance tracking, handover documentation and client-facing project delivery across complex international environments.
Focus
What I bring
Technology Risk & GRC
Governance, controls, risk assessment, policy, compliance, evidence and assurance.
Information Security
ISO/IEC 27001, IAM, MFA, Conditional Access, monitoring, endpoint security and resilience.
Audit & Management Systems
Risk-based auditing, control effectiveness, NCR/CAPA, root cause analysis and continual improvement.
IT Governance
Microsoft 365, Entra ID / Azure AD, SharePoint, Atera, Veeam, Defender, VMware, Proxmox and secure remote access.
Credentials
Professional development
ISO/IEC 27001 Lead Implementer
Certified 2026 · Valid through 2029
Security+
SY0-701 · Valid through 2027
Professional Diploma in Cybersecurity
Distinction
Bachelor of Business in Management
Distinction
ISO 9001:2015 Internal Auditor
Certified training course
Higher Diploma in Cybersecurity Risk & Compliance
Commencing September 2026
Additional qualifications include a Level 6 Electrical craft qualification and IOSH Managing Safely.
Writing
Thinking out loud
Governance · Career
What quality management taught me about cybersecurity
Why governance, evidence, ownership, auditability and continual improvement translate surprisingly well from quality management into information security.
Coming soon →
Security · Controls
Security controls have to work for people
Why technically correct controls still fail when they ignore real workflows, usability and organisational culture.
Coming soon →
Career · GRC
From engineering to governance, risk & cybersecurity
A career transition built less on starting again and more on recognising the transferable thread running through the work.
Coming soon →Contact
Let's talk
Open to conversations around governance, risk, compliance, cybersecurity assurance and technology risk. Based in Wicklow, Ireland.